 Managed IT Services

IT Support for Insurance Brokers in NJ
Your agency holds driver’s licenses, dates of birth, medical questionnaires and bank details for thousands of households — under a regulator that expects you to protect them. We keep independent New Jersey agencies secure, compliant and open for business.
Why Insurance Agencies Need More Than Generic IT Support
Most firms selling IT support for insurance brokers treat an agency like any other twelve-person office: a few laptops, a printer, email. That misses what actually sits in your systems. A retail agency holds more sensitive personal information per employee than almost any small business in New Jersey — Social Security numbers on life applications, medical history on health cases, driver’s license numbers and VINs on every auto policy, loss runs on commercial accounts, and bank account details for EFT premium payments.
It also misses how you work, which is the first thing IT support for insurance brokers has to get right. Your agency management system is the business. When Applied Epic is slow on a Monday morning, nobody is quoting, nobody is servicing renewals, and the carrier download that should have posted overnight is sitting in a queue. IT support for insurance brokers in NJ has to start from the AMS and work outward, not the other way around.
And it misses who is watching. The New Jersey Department of Banking and Insurance regulates you. If you also hold a New York license — and plenty of North Jersey agencies write New York business — you are a NYDFS covered entity with prescriptive cybersecurity rules on top. That combination is why insurance agency IT solutions New Jersey firms actually need look different from a generic managed services plan, and why IT support for insurance brokers in NJ is a specialty rather than a label.
NJ DOBI Cybersecurity Compliance: What Is Actually Expected
Any honest conversation about IT support for insurance brokers in NJ starts with the regulator closest to home. The Department of Banking and Insurance issued Bulletin 22-05 to every individual and entity it regulates — insurers, producers, banks, credit unions and money transmitters alike. It is a directive to review your program, and it names the controls it expects you to have:
- Multi-factor authentication on the systems that matter, called out by name as a core measure
- Incident response and business continuity planning that specifically addresses ransomware
- A full test of your ability to restore systems and data from backup — not a backup report, an actual restore
- Employee cybersecurity awareness training as an ongoing program
- Sanctions monitoring, including OFAC screening in your transaction processes
Read that list again as an agency principal. Most of it is IT support for insurance brokers work you would have to delegate anyway, and the restore test is the one nearly every agency fails the first time we run it. NJ DOBI cybersecurity compliance has no small-agency exemption either — the bulletin applies to the six-person shop in Cedar Grove the same way it applies to a carrier.
It is guidance rather than a statute with its own penalty schedule, which leads some agencies to shelve it — and leads their IT support for insurance brokers provider to never mention it. That is a mistake for a simpler reason: your carriers, your E&O underwriter and your cyber insurer are all asking the same questions, and they do have consequences. Our NJ Regulation 22-05 compliance guide breaks the requirements down line by line.
If You Hold a New York License, NYDFS Part 500 Applies Too
Any producer licensed by New York is a covered entity under 23 NYCRR Part 500, and the requirements are specific rather than advisory. Since November 1, 2025, covered entities must apply multi-factor authentication to all information-system access and maintain a documented asset inventory recording each system’s owner, location, classification and recovery objectives.
Smaller agencies get a limited exemption — fewer than 20 employees and contractors, under $7.5 million in gross revenue for three years, or under $15 million in assets — but read what it actually does. It narrows the MFA requirement to remote access and privileged accounts. It does not remove it. Cybersecurity for independent insurance brokers NJ agencies with a New York book is therefore a two-regulator problem, and IT support for insurance brokers in NJ has to account for both.
Pennsylvania Agencies Have a Written-Program Statute
If your agency is licensed across the Delaware, Pennsylvania adopted the NAIC Insurance Data Security Model Law, which requires a written information security program based on a documented risk assessment. Licensees with fewer than ten employees, including independent contractors, are exempt from building the full program. New Jersey has not adopted that model, which is why the two states feel so different to comply with — and why IT support for insurance brokers across the river needs a different checklist.
Where the FTC Safeguards Rule Fits — and Where It Does Not
Agencies hear about the FTC Safeguards Rule from their accountant or from a vendor questionnaire and assume it applies to them. Under the Gramm-Leach-Bliley Act, insurance activities are generally overseen by state insurance regulators rather than the FTC, so FTC Safeguards Rule compliance for independent brokers is not the automatic answer it is for a CPA firm.
It can reach you if your agency also runs premium finance or other non-insurance financial services. This is a question for your counsel, not your IT provider — but the security program the rule describes is close enough to what DOBI, NYDFS and your carriers want that building it once covers you either way. We do that work as written information security plan engagements.
Agency Management System Cybersecurity and Support
Your AMS is where the regulated data lives, which makes agency management system cybersecurity the centre of the whole program. It is also the application your staff will judge us on, and the reason IT support for insurance brokers starts there. Here is how we handle the platforms New Jersey agencies actually run.
Applied Epic Cloud Hosting Solutions
Whether you run Epic in Applied’s cloud or on a server in your back office, the questions are the same: who can reach it, from where, with what authentication, and what happens the morning it will not start. For hosted agencies we secure the path in — MFA, conditional access, managed endpoints — because the platform vendor secures their side and yours is still yours. For on-premises agencies, IT support for insurance brokers covers the server, the SQL database behind it, backup with tested restores, and a documented plan for moving to Applied Epic cloud hosting solutions when the hardware reaches end of life.
Vertafore AMS360 IT Support
AMS360 agencies tend to call us about the same three things: sign-on problems after a password policy change, document management performance when the attachment store grows, and carrier download failures that turn out to be a network or security-software conflict rather than a Vertafore issue. Vertafore AMS360 IT support means owning that diagnosis instead of leaving you on a three-way call trying to prove whose problem it is — which is what separates IT support for insurance brokers from a generic help desk.
EZLynx Software Integration Support NJ
EZLynx is browser-delivered, which agencies assume removes IT from the equation until a rater stops talking to a carrier site, a scan-to-email workflow breaks, or staff start sharing one login because single sign-on was never set up. EZLynx software integration support NJ agencies need is mostly identity, browser policy and the integrations around the edges — email, e-signature, document storage and the phone system.
HawkSoft, QQCatalyst, NowCerts and the Rest
We are vendor-independent by design, because IT support for insurance brokers should not depend on which platform you signed with. The same discipline applies to HawkSoft, QQCatalyst, NowCerts or whatever your agency migrates to next: know where the data sits, control who reaches it, prove you can restore it, and keep the integrations that touch it inside the security program.
Why Is My Agency Management System Running Slow?
It is rarely the AMS. In agencies we take over, the usual culprits are an under-provisioned server or workstation, a security product scanning the database in real time, saturated or misconfigured Wi-Fi in a converted-house office, a document store that outgrew its disk, or an internet circuit with no failover that degrades before it fails. We measure before we replace anything, because good IT support for insurance brokers in NJ should cost you a setting change rather than a purchase order.
Secure Email Solutions for Insurance Agents
Email is where an agency’s risk concentrates. Applications arrive by email, loss runs go out by email, and premium finance and EFT instructions move by email. Criminals know the pattern — the FBI’s Internet Crime Complaint Center logs the results every year — and an agency’s domain is an easy thing to forge if nobody providing your IT support for insurance brokers has locked it down.
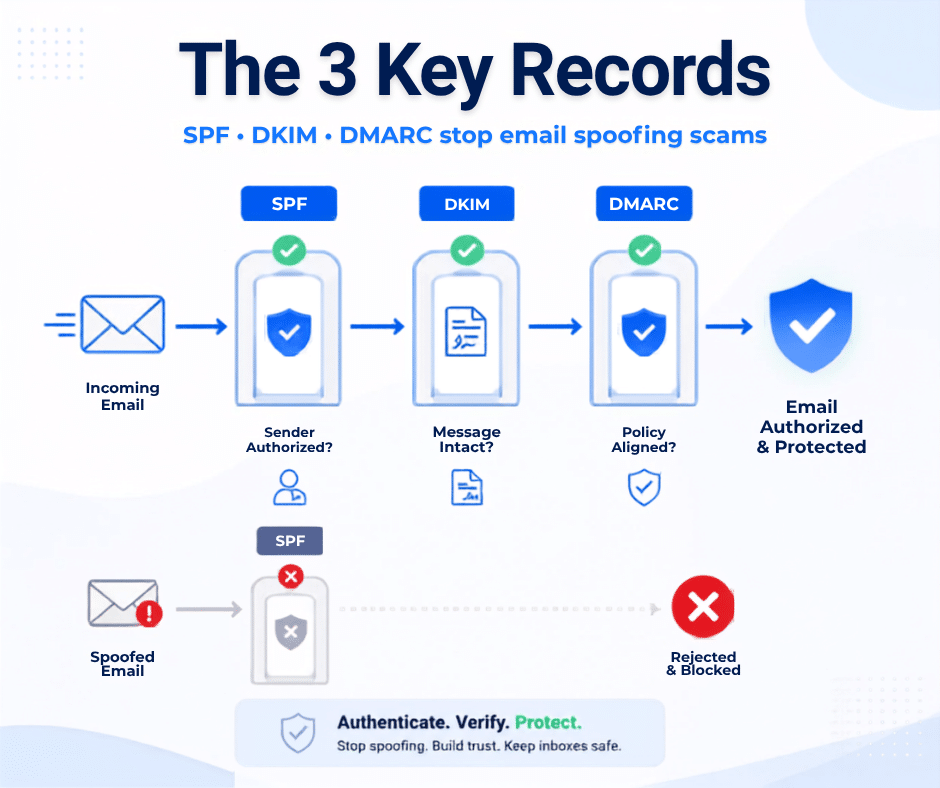
Secure email solutions for insurance agents start with three DNS records almost no agency has configured correctly — SPF, DKIM and DMARC — which together decide whether a stranger can send mail that appears to come from your agency. On top of that sits encryption for anything carrying a Social Security number or medical history, retention and archiving so a message can be produced years later, and the human layer: a policy that no change to payment instructions is accepted without a callback to a known number.
This matters twice over for an agency. You are a target, and you are also the party a client will blame when a forged message costs them money. The same controls that satisfy your carrier’s security questionnaire prevent the phone call you never want to take, which is the plainest argument for specialised IT support for insurance brokers.
Data Breach Prevention for Insurance Agencies
Data breach prevention for insurance agencies is less about exotic tooling than about doing a short list of unglamorous things consistently. The list below maps directly onto what Bulletin 22-05 tells you to review — which is the point.
| Control | What it stops | What the regulator expects |
|---|---|---|
| Multi-factor authentication everywhere | Stolen passwords becoming mailbox takeovers | Named explicitly in DOBI Bulletin 22-05; mandatory under NYDFS |
| Managed detection and response | Ransomware spreading from one workstation to the AMS server | Ransomware-specific incident response planning |
| Tested backup and restore | A recovery that fails when you need it | A full restore test, not a backup report |
| Security awareness training | The click that starts most incidents | Ongoing employee training |
| Documented asset inventory | Unknown devices holding client data | Required for NYDFS covered entities since November 2025 |
| Written incident response plan | Improvised decisions during a breach | Incident response and business continuity planning |
Notice what is not on the list: nothing here requires an in-house security team, only IT support for insurance brokers that runs the controls for you. It requires a partner who runs the controls and keeps the evidence, so the answer to a carrier questionnaire is a document rather than a memory. A security risk assessment is how we find out which of the six you already have.
Managed IT Services for New Jersey Insurance Agencies
Everything above is delivered as one flat-rate program rather than a stack of projects, so IT support for insurance brokers in NJ is a monthly line item you can budget. Managed IT services for New Jersey insurance agencies, the way we run them, come down to three commitments.
Keep the Agency Running
A help desk your producers can reach without a ticket portal ritual, managed workstations and servers, monitored backups with restores we actually test, and someone who knows your AMS vendor’s support process. Renewals do not wait for IT.
Keep the Agency Defensible
MFA, managed detection and response, encrypted email, security awareness training, asset inventory and a written incident response plan — maintained continuously, with the documentation kept current so a questionnaire is a retrieval task rather than a project.
Keep the Agency Moving
Technology planning that matches how agencies grow: a server that ages out before it fails, an office move that does not lose a day of production, and a plan for the systems consolidation that follows an acquisition — in either direction.
Most agencies come to us running a mix of the three badly, usually because their previous IT support for insurance brokers arrangement was a friend of the owner’s son. The first ninety days of IT support for insurance brokers are about closing the gaps that would fail a questionnaire today, then putting the routine in place that keeps them closed. See managed IT services for how the program is structured, or co-managed IT if you already have someone internal.
VoIP Phone Systems for Insurance Agencies
An agency lives on the phone, which is why IT support for insurance brokers includes the phone system. Claims calls, renewal calls, the callback that verifies a change of payment instructions — all of it runs through a system most agencies inherited and nobody has reviewed since.
VoIP phone systems for insurance agencies should do a few specific things: ring a producer’s cell without exposing their mobile number, keep call recording where your E&O carrier would want it, route after-hours claims calls properly, and survive an internet outage by failing over rather than going dark. We design and support them alongside the network as part of IT support for insurance brokers, which is the only way the quality problems get solved rather than blamed on the carrier.
More on our business VoIP service, and on disaster recovery for the outage that takes the phones with it.
HIPAA Compliant IT Support NJ Benefits and Health Brokers Need
If your agency writes group health, Medicare or employee benefits, you are handling protected health information and you may be a business associate of the plans you serve — which brings HIPAA’s Security Rule into scope alongside the insurance regulators. Enrollment forms, claims questions and medical underwriting all leave PHI in your email and your AMS.
HIPAA compliant IT support NJ brokers need is not a separate product from IT support for insurance brokers. It is the same controls with the documentation HIPAA asks for: a risk analysis, safeguards mapped to it, a business associate agreement with vendors who touch PHI, and a breach notification process with its own clock. We run that work through our HIPAA compliance consulting practice, which supports medical practices across the same counties.
Life and annuity agencies have a lighter version of the same problem — medical questionnaires on applications are health data even when HIPAA does not reach you, and your clients will judge you by how they are handled.
Insurance Agency IT Solutions New Jersey Firms Can Get in Person
eMDTec has supported New Jersey businesses since 2002 from our office at 155 Pompton Ave in Verona, and we sit on the board of the North Essex Chamber of Commerce. We work with agencies across Essex, Bergen, Morris, Union, Passaic and Hudson counties — from Verona, Montclair and Livingston out to Paramus, Hackensack and Newark, down the Route 1 corridor toward Princeton and Trenton, and along the Shore where seasonal property books create their own storm-season IT problems.
Local matters more in this business than in most, which is why IT support for insurance brokers in NJ should come with a van and a drive time. When a wire-fraud scare lands at four o’clock on a Friday, or a storm takes an office offline during renewal season, you want someone who can be at your door rather than a ticket in a queue three time zones away. Start with our Essex County coverage, or see which NJ regulations apply to your business.
We also support the firms your agency works beside every day — financial services firms, law firms and accounting practices — which means the compliance vocabulary behind IT support for insurance brokers is already ours.
Find Out Where Your Agency Stands
We will walk your agency through the Bulletin 22-05 checklist, tell you which items you would pass today and which you would not, and show you what it takes to close the gap — whether you hire us or not.
Frequently Asked Questions About IT Support for Insurance Brokers in NJ
How do insurance brokers comply with the FTC Safeguards Rule?
First, confirm whether it applies. Under Gramm-Leach-Bliley, insurance activities are generally regulated by state insurance authorities rather than the FTC, so many agencies are covered by DOBI and NYDFS instead. If your agency also runs premium finance or other non-insurance financial services, the rule can reach you — ask your counsel. Either way the answer is the same program, and the same IT support for insurance brokers behind it: a written security plan with a named owner, a risk assessment behind it, MFA, encryption, vendor oversight, training, and an incident response plan you have tested.
Why is my agency management system running slow?
Usually something around the AMS rather than the AMS itself — an over-subscribed server, security software scanning the database in real time, Wi-Fi that cannot carry the office, a document store that has outgrown its disk, or a single internet circuit degrading without failover. We measure first; IT support for insurance brokers that starts with a stopwatch usually ends with a configuration change rather than new hardware.
Best backup solutions for independent insurance agencies?
The one you have restored from recently. For an agency that means image-level backup of the AMS server and anything it depends on, a copy held off-site and immutable so ransomware cannot encrypt it, retention that matches your record-keeping obligations, and a documented restore test at least annually — which DOBI asks for by name and which your IT support for insurance brokers provider should be scheduling.
Do insurance brokers need cyber liability insurance for themselves?
You know the answer better than we do, and you have seen what a claim looks like from the carrier side. What is worth knowing is that underwriters now price agency policies on the same controls DOBI lists — MFA, tested backups, training, incident response. Agencies that implement them often find the renewal conversation easier, which is one of the few times IT support for insurance brokers pays for itself directly.
Does the NJ DOBI cybersecurity bulletin apply to a small agency?
Yes. Bulletin 22-05 was issued to all individuals and entities the Department regulates, with no exemption based on headcount or revenue. The Department acknowledges not every measure fits every entity, but a six-person agency is squarely within scope.
We are licensed in New York as well. What changes?
You become a NYDFS covered entity under 23 NYCRR Part 500. Since November 1, 2025 that means MFA on all information-system access and a documented asset inventory. Agencies under 20 employees, or under $7.5 million in revenue, or under $15 million in assets qualify for a limited exemption that narrows MFA to remote and privileged access rather than removing it.
Can you work with our agency management system vendor?
Yes, and we expect to. We are vendor-independent, which means we own the diagnosis with Applied, Vertafore, EZLynx or whoever hosts your platform rather than handing you back a ticket number. Most of what looks like an AMS problem turns out to be identity, network or security-software related — all of it inside the scope of IT support for insurance brokers.
How disruptive is switching IT providers for an agency?
Handled properly, a change of IT support for insurance brokers provider is invisible to your producers. We document first, take over monitoring and backup before touching anything else, and schedule anything with downtime outside business hours — and away from renewal peaks and open enrollment.
Do you support remote and hybrid producers?
Yes. Secure remote access to the AMS, managed laptops, MFA, and phones that follow the producer are standard parts of IT support for insurance brokers rather than add-ons. See remote workforce IT support.
What does IT support for insurance brokers in NJ cost?
IT support for insurance brokers in NJ is priced per user, per month, so it scales with headcount rather than with the number of incidents. What moves the number is how much regulated data you hold, whether you run your AMS on-premises, and how much documentation you need us to maintain. We quote after a walkthrough, not before.
A Compliance-First IT Partner for NJ Agencies Since 2002
eMDTec has kept New Jersey’s regulated small businesses secure, documented and productive for more than two decades, from our office in Verona.
Talk to an Engineer
Start a Conversation and Learn How Technology Can Transform Your Business
Reach out today to schedule a meeting where we'll learn about your business and create an IT action plan that works for you.
Schedule Your Free Consultation Call (973) 295-5570