 Managed IT Services

Free Network Vulnerability Scan & Cybersecurity Assessment in New Jersey
Is your New Jersey business truly protected against modern ransomware and data breaches? Our non-invasive risk analysis reveals hidden infrastructure vulnerabilities, data exposures, and regulatory compliance gaps. It is the cybersecurity assessment New Jersey owners can request in two minutes, with no software installation or administrative credentials required.
Secure Your Business Network Before Cybercriminals Exploit It
Targeted cyberattacks against small and mid-sized businesses surged dramatically over the past year. Modern threat actors rarely target major enterprises first; instead, they exploit SMBs that mistakenly assume they are too small to notice. The free cybersecurity assessment New Jersey firms request from eMDTec exists to close that gap before an attacker finds it.
A professional network security health check from eMDTec delivers concrete facts about your perimeter defenses. Our certified engineers leverage enterprise-grade scanning tools to expose network vulnerabilities that standard IT monitoring utilities miss entirely. Whether your team operates out of a single medical office or a multi-location accounting firm, we map our findings directly to your industry’s specific threat landscape.
The result is not a 40-page technical dump. You get a prioritized, plain-language risk summary, a 30-minute debrief with the engineer who ran the scan, and a clear answer to the question every owner actually asks: what should we fix first? That is the standard every cybersecurity assessment New Jersey clients receive from us is held to.
What Is Included in a Small Business Cyber Risk Audit?
Knowing your technical vulnerabilities can feel overwhelming, but protecting your data, reputation, and clients requires a clear roadmap. A small business cyber risk audit should tell you three things: where you are exposed from the outside, what an attacker could reach once inside, and which of those findings your regulator, auditor, or cyber insurer will ask about. That is the scope of every cybersecurity assessment New Jersey businesses commission from us, free or comprehensive. We offer two distinct tiers of analysis to match your current operational needs and regulatory obligations.
Both tiers of our cybersecurity assessment New Jersey service are run by the same engineers, use the same reporting format, and feed the same remediation roadmap. Most clients start with the free perimeter assessment and move to the comprehensive engagement when a compliance deadline, an insurance renewal, or a board question makes documented evidence necessary.
1. Free Perimeter Security Assessment
Best for: NJ small businesses requiring a rapid, high-level threat evaluation with zero cost or operational disruption.
- External vulnerability scan. We analyze your outward-facing IP addresses and domain for open ports, exposed services, and unpatched system flaws.
- Dark web credential audit. We check whether employee corporate emails or passwords have been leaked in historical third-party data breaches.
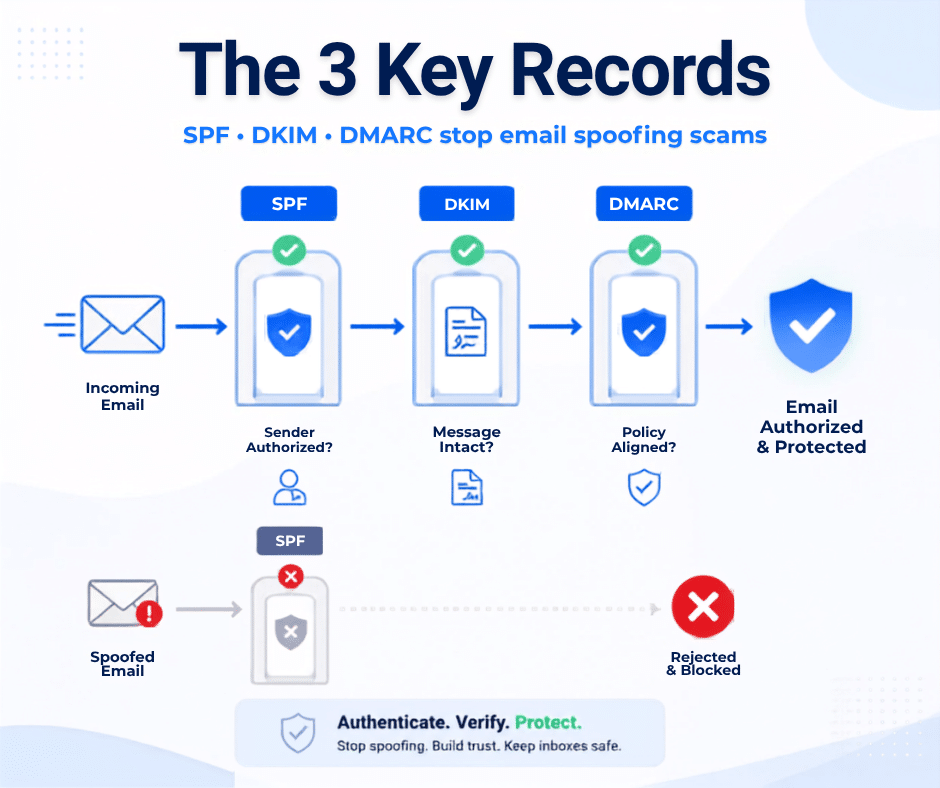
- Email authentication review. We audit your domain’s SPF, DKIM, and DMARC configurations to stop phishing and email spoofing.
- 30-minute engineering debrief. You receive a plain-language executive summary prioritizing your top security exposures.
2. Comprehensive Security Risk Assessment
Best for: Regulated practices requiring definitive evidence for compliance auditors, board reviews, or cyber insurance renewals.
- Internal network penetration testing. We safely simulate internal lateral movement to see how far an attacker could get once inside.
- Active Directory and identity security review. We audit credential hygiene, stale accounts, and multi-factor authentication (MFA) enforcement gaps.
- Regulatory compliance gap analysis. We measure your operational controls directly against HIPAA, PCI DSS v4.0, or FTC Safeguards.
- WISP readiness evaluation. We review your Written Information Security Program to ensure alignment with state and federal law.
- Full remediation roadmap. A complete, documented risk report providing step-by-step technical fixes for your infrastructure.

How Does a Free Network Vulnerability Scan Work?
According to CISA’s cyber hygiene guidance, organizations that conduct regular vulnerability assessments reduce their total breach risk by up to 70%. We make the process straightforward, completely non-disruptive, and highly actionable. A free network vulnerability scan from eMDTec runs entirely from outside your perimeter, which is why it needs no agents, no admin passwords, and no maintenance window.
Every cybersecurity assessment New Jersey clients book with us follows the same five steps, from a two-minute form to a plain-language debrief. Most engagements complete within a few business days of the initial conversation.
Quick Request
Submit your organization’s domain name through our secure form in under two minutes. That is all a cybersecurity assessment New Jersey businesses request from us needs to begin, with no commitment and no sales call to book first.
External Analysis
Our engineers launch a non-invasive external scan of your public IP space and domain. This requires zero administrative access and zero network downtime.
Breach Intelligence Gathering
We run comprehensive data-broker and dark web sweeps to discover active corporate credential leaks tied to your domain.
Email Security Validation
We test your mail domain to confirm outside attackers cannot forge or spoof your company email addresses, then document any SPF, DKIM, or DMARC gaps.
Plain-Language Debrief
We present our core findings during a brief consultation, walking you through a prioritized action plan tailored to your business goals and compliance obligations.
Specialized Compliance Auditing Built for Regulated Verticals
Generic IT support is no longer enough to satisfy modern regulatory bodies. Our security assessments focus heavily on the strict data privacy frameworks governing professional services in New Jersey: HIPAA and HITECH for healthcare, the FTC Safeguards Rule and IRS Publication 4557 for accounting, NJ DOBI Regulation 22-05 and SEC and FINRA rules for finance, and the confidentiality obligations that govern law firms. The cybersecurity assessment New Jersey regulators and auditors will accept is the one that maps findings to the specific rule you answer to.
Is Your Practice Ready for a HIPAA Security Risk Assessment?
Our engineers ensure your Electronic Medical Record (EMR) systems and network backups are fully isolated and encrypted, keeping patient data aligned with HIPAA and HITECH compliance guidelines. The HIPAA security risk assessment NJ practices must document under 45 CFR 164.308 is not optional, and it is the first thing an OCR investigator requests after a breach. The free cybersecurity assessment New Jersey practices use as a starting point surfaces the external exposures that belong in that document; the comprehensive engagement produces the full risk analysis itself.
Practices on CGM eMDs, eClinicalWorks, or a cloud EHR get the same treatment: we check whether the EHR vendor holds a signed Business Associate Agreement, whether remote access to the chart is protected by MFA, and whether backups would actually restore after ransomware. This work is paired with our healthcare IT support and HIPAA compliance consulting so nothing falls between the assessment and the fix.
FTC Safeguards Vulnerability Scan Requirements for Accounting and CPA Practices
We analyze your network infrastructure to verify it fulfills the data security requirements mandated by the IRS Safeguards program and the FTC Safeguards Rule before peak tax season. The rule requires either continuous monitoring or a vulnerability scan every six months plus annual penetration testing, and most small firms have neither. An FTC Safeguards vulnerability scan from eMDTec gives you the dated evidence the rule asks for, and it doubles as the technical section of your Written Information Security Program.
Tax professionals who need the WISP itself can pair the cybersecurity assessment New Jersey CPAs get from us with our WISP compliance services and our FTC Safeguards Rule compliance program, both built for the same firms we support through IT support for accounting firms.
NJ DOBI Regulation 22-05 Compliance for Finance and Wealth Management
We evaluate your administrative and technical controls to ensure your firm is fully prepared for NJ DOBI Regulation 22-05 audits, FINRA compliance reviews, and SEC cybersecurity mandates. NJ DOBI Regulation 22-05 compliance applies to insurance licensees and other DOBI-regulated entities, and it requires a documented risk assessment, a written information security program, MFA on remote access, and a defined breach notification process; the Department expects to see the assessment the program was built on. Broker-dealers and RIAs answer to FINRA and the SEC instead, but the technical evidence they need is the same.
For broker-dealers, RIAs, and insurance producers, the free cybersecurity assessment New Jersey firms can request here is the quickest way to find out whether your public-facing systems would survive a regulator’s first look. Firms that need the full documented program work with our financial services IT support team and, for advisory practices, our IT support for wealth management firms.
Law Firm Data Breach Prevention and Attorney-Client Privilege
We protect attorney-client privilege by identifying vulnerabilities in secure document management systems, cloud file repositories, and the remote-access VPN connections used by staff. Law firm data breach prevention starts with the boring findings: an old remote desktop port left open, a partner’s email address in a 2019 breach dump, a DMARC record that lets anyone spoof the firm to a client’s bookkeeper. Those are exactly what a cybersecurity assessment New Jersey law firms request from eMDTec finds first.
The comprehensive engagement adds the internal view, including who can read which matter folders, whether litigation-hold data is backed up immutably, and whether e-signature and billing integrations expose client data. It sits alongside our IT support for law firms.
Why Regulated NJ Businesses Trust eMDTec
A scan is only as useful as the people reading it. The cybersecurity assessment New Jersey owners get from a national lead-generation site is a PDF and a sales call; the one you get from us is read by an engineer who has fixed the same findings in offices like yours and who can be in your building if the fix needs hands.
Certified Security Engineers
Your assessment is led by veteran engineers holding CompTIA Security+, CISSP, and specialized Microsoft security certifications, not entry-level analysts reading a template.
Zero Operational Disruption
Our foundational assessments execute completely from outside your network perimeter. There are no software agents to install and no risk of network sluggishness during the workday.
Established Local Reputation
Headquartered in Verona since 2002, eMDTec has spent more than two decades defending New Jersey healthcare practices, law firms, and financial firms against evolving digital threats.
Plain-Language Results
Every cybersecurity assessment New Jersey report we deliver is written for owners and decision-makers, with each finding ranked by risk and a clear order of remediation, so you know exactly where to start.
What Happens After the Cybersecurity Assessment?
Every cybersecurity assessment New Jersey clients complete with us ends the same way: a short list, usually five to ten items, ordered by how likely each one is to cause an incident and how hard it is to fix. Some are ten-minute changes your current IT person can make the same afternoon, like turning on DMARC enforcement or closing a forgotten port. Others, such as replacing an end-of-life firewall or rolling out MFA across a practice, become projects.
You are free to hand that list to anyone. Many firms use the cybersecurity assessment New Jersey cyber insurers now ask about at renewal as the checklist for their existing provider. Others ask us to quote the remediation, and some decide it is time for a managed relationship, where the cybersecurity and threat defense work is continuous rather than annual. There is no wrong answer, and there is no pressure at the debrief.
Two findings come up in almost every cybersecurity assessment New Jersey offices ask us for. The first is email: a domain with no DMARC enforcement, which means anyone can send mail that looks like it came from the owner, and a surprising number of wire-fraud cases start exactly there. The second is credentials: a staff password from an old LinkedIn or Adobe breach that still works on the practice management login because nobody was ever told to change it. Neither takes long to fix, and both show up on the report before you spend a dollar.
For firms that want a recurring cybersecurity assessment New Jersey auditors can rely on, we re-run the external scan and dark web sweep quarterly, re-test email authentication whenever the domain changes, and keep the risk register current so the next audit, renewal, or board question is a document you already have. You can also check your own domain today with our free domain scanner.
Don’t Wait for a Breach to Find Your Gaps
Cyberattacks do not wait for you to be ready. The free cybersecurity assessment New Jersey businesses request here costs nothing and takes two minutes; skipping it is the expensive option. Get a clear picture of your security posture within a few business days.
Start Your Free Cybersecurity Assessment: Fill Out the Form Below
Fill out the form below to request the free cybersecurity assessment New Jersey businesses trust. No admin credentials or software installation are required. Our security team will follow up within one business day to confirm the assessment and walk you through the process.
Cybersecurity Assessment New Jersey: Frequently Asked Questions
How much does a cybersecurity assessment cost in New Jersey?
The entry-level cybersecurity assessment New Jersey businesses request most is free, with no software to install, no obligation, and no sales pressure. It gives you an honest snapshot of your exposure and a prioritized list of what to fix first. Firms with regulatory requirements often follow it with a comprehensive security risk assessment covering HIPAA, PCI DSS, FTC Safeguards, and SOC 2 readiness, which is scoped and priced to your environment.
What does the free cybersecurity assessment include?
In every free cybersecurity assessment New Jersey businesses receive from us, we evaluate the areas attackers probe first: your external attack surface, email authentication and phishing exposure, and dark web exposure of your company credentials, plus a compliance-gap read for HIPAA, PCI, or WISP readiness. You receive a plain-language report with each finding ranked by risk, then a 30-minute debrief with the engineer who ran it.
How is this different from a full security risk assessment?
Think of the free cybersecurity assessment New Jersey businesses start with as the diagnostic and the full risk assessment as the complete physical. The free version finds your most urgent external exposures fast. The comprehensive version tests from inside the network, documents your entire compliance posture against frameworks like the NIST CSF 2.0, and produces the evidence auditors, regulators, and cyber insurers require.
Do you need admin credentials or access to our network?
Not for the free cybersecurity assessment New Jersey businesses start with. Everything runs from outside your perimeter using your domain name and public IP addresses, which is why there is nothing to install and no risk of slowing anyone down. The comprehensive engagement does require supervised internal access, and we scope that with you in advance.
How long does the assessment take?
Most free cybersecurity assessment New Jersey engagements are completed within a few business days of our initial conversation, with zero disruption to your team. In-depth engagements typically run one to two weeks depending on the size of your environment and how many locations are in scope.
Does a HIPAA security risk assessment have to be done every year?
HIPAA requires the risk analysis to be accurate and current rather than tied to a calendar, but OCR guidance and most auditors treat an annual review, plus a fresh one after any major change, as the standard. Our free scan is a fast way to check whether last year’s analysis still reflects reality; the comprehensive assessment produces the updated document itself.
Will the cybersecurity assessment help with our cyber insurance application?
Yes. Carriers now ask specific questions about MFA, backups, email security, and endpoint protection, and they increasingly verify the answers. A documented cybersecurity assessment New Jersey underwriters can review is the cleanest way to answer them, the findings and roadmap give you a defensible basis for every line on the form, and we can supply the technical attestations your broker requests.
Where can I learn more about cyber threats facing NJ businesses?
Two resources we recommend: the New Jersey Cybersecurity & Communications Integration Cell (NJCCIC), the state’s own threat-intelligence hub, and CISA’s free cyber hygiene services. When you are ready for a cybersecurity assessment in New Jersey performed by a local team, contact eMDTec or explore our full cybersecurity services.
Cybersecurity Assessment New Jersey Businesses Can Book Locally
As cyber threats continue to evolve in 2026, New Jersey businesses face increasingly sophisticated ransomware, phishing, and supply chain attacks. Every cybersecurity assessment New Jersey clients receive from our certified engineers is built on the NIST Cybersecurity Framework 2.0, so we evaluate your defenses, identify critical gaps, and provide a clear remediation roadmap, so you can protect your data, your clients, and your reputation.
We work from Verona in Essex County and serve businesses across Northern and Central New Jersey, including Essex County, Morris County, Bergen County, Hudson County, Union County, and Passaic County, plus the greater Tri-State area. If your office is in Clifton, Wayne, or Paterson, start with our local cybersecurity and managed IT services for Passaic County, NJ.
Ready to see where you stand? Request the free scan above, or call 973-295-5570 and ask for an engineer. Either way, the cybersecurity assessment New Jersey firms trust starts with a conversation, not a contract.
Start a Conversation and Learn How Technology Can Transform Your Business
Reach out today to schedule a meeting where we'll learn about your business and create an IT action plan that works for you.
Schedule Your Free Consultation Call (973) 295-5570